Friends who do cross-border charging product business have most likely encountered these troublesome issues: the supplier you negotiated with ships the goods, but they are detained by customs after arriving at the port, and you either face a fine or have the goods directly destroyed; a charger that you finally managed to list is suddenly removed from the platform, and your deposit is deducted; even worse, the charging cables you sold have safety issues, leading to consumer claims and mass recalls. Many people think that asking suppliers for a few certification certificates equals compliance, but in fact, this is only the most basic step. What can really help you avoid risks is a systematic supplier regulatory audit.
Beginner Basics: What an Audit Is, Why It Is Done, and Who It Is For
When first exposed to regulatory audits, many people easily confuse them with quality audits and single product tests. Clarifying the core concepts first will prevent you from going off track later.
Plain-Language Definition and Core Differences
Simply put, a supplier regulatory audit is a systematic inspection used to verify whether your charging product supplier can meet the legal access requirements of the target market. It is completely different from the quality audits and single product tests we often talk about:
The difference from a quality audit is that a quality audit focuses on whether the product is well-made, durable, and meets performance standards, while the core of a regulatory audit is “whether it can be sold legally”, which checks access qualifications rather than product performance. For example, a charging cable that is unbreakable and charges fast is of good quality, but if its lead content exceeds the limit and does not meet EU RoHS requirements, it cannot be sold no matter how good the quality is.
The difference from a single test and factory audit is that a single test only checks whether the submitted sample can pass, and a factory audit only looks at the factory’s status on the day you visit. A regulatory audit, however, evaluates the supplier’s continuous compliance capability — it is not enough for the sample to pass this time; every batch of mass-produced goods must meet the requirements, without secretly replacing materials or moving the factory.
Four Types of Real Risks of Not Conducting Audits
Many people think audits are a waste of time and money, and only realize how high the cost is when problems actually occur. There are four common types of risks:
The first type is customs and regulatory risks, triggered by the customs or regulatory authorities of the target market. Regulatory authorities may take measures such as detention, sales ban, recall, rectification, or penalty. The specific consequences depend on the applicable regulations and the circumstances of the case.
The second type is channel access risks, triggered by e-commerce platforms or offline retailers. For example, platforms like Amazon and Walmart will check the compliance qualifications of products. If they do not meet the requirements, the products will be directly removed from the shelves, traffic will be restricted, deposits will even be deducted, and in severe cases, the store will be closed.
The third type is product safety risks. If a product has compliance defects, such as a charger with insufficient insulation causing electric leakage that injures consumers, it will trigger mass recalls and civil compensation, the cost of which is often much higher than the payment for the goods.
The fourth type is supply chain liability risks. Now more and more countries and regions have introduced supply chain due diligence regulations, such as relevant EU provisions. However, supply chain due diligence obligations usually only apply to specific entities; whether downstream enterprises are liable shall be judged based on specific regulations, fault, entity identity, and contractual agreements, and they do not automatically bear joint and several liability. It cannot be simply assumed that importers and sellers will necessarily bear joint and several liability after a supplier violates regulations.
Scope and Boundaries of Application
The audit checklist discussed in this article is specifically for charging products. Applicable products include charging cables, USB/USB-C data cables, chargers, power adapters, and related connectors such as USB-C terminals.
Applicable suppliers are not limited to manufacturing factories, but also include OEM/ODM factories, traders, and even key component suppliers such as USB-C interface factories — after all, the compliance of core components directly affects the compliance of the entire product.
There are four main applicable scenarios: when onboarding new suppliers, annual re-evaluation, when changing sales markets or product models, and re-audits after compliance incidents occur.
It should be noted that this checklist does not apply to non-charging electronic products such as toys and children’s products. Compliance requirements vary greatly across different categories, so do not apply it directly.
Pre-Audit Preparation: Build a Framework First and Then Classify Risks, Don’t Jump Straight to Checking the Checklist
Many people start by taking a long checklist and asking suppliers for materials, only to end up either checking a bunch of useless items or missing key ones. The correct approach is to first build a regulatory framework suitable for yourself, classify risks, and then conduct targeted audits. This can both control risks and save costs.
Core Elements for Determining Regulatory Applicability
Not all regulations apply to your products. To determine whether a requirement needs to be checked, there are three core basic dimensions: which market you are selling to, the functional parameters of the product itself, and the cooperation mode between you and the supplier (for example, private label or OEM, B2C or B2B).
For charging products specifically, the core determination details include key indicators such as input voltage, output power, port type, whether it has wireless function, whether it contains a battery, plug type, sales date, and sales country. Listing this information allows you to quickly filter out inapplicable regulations.
Product Risk Classification Scoring Method
Different products have different compliance risks, and the intensity of audits should also be different. You can use an internal risk control scoring method to classify products, without conducting a full audit every time.
There are 7 commonly used scoring dimensions, each scored 0-2 points. The higher the score, the higher the risk. Core reference indicators include whether it is connected to mains electricity, power level, whether it has wireless or battery functions, etc. Enterprises can supplement dimensions according to their own product characteristics, with a total full score of 14 points.
The classification thresholds can be adjusted according to your own risk preference. Generally speaking: 0-5 points is low risk, 6-10 points is medium risk, and 11-14 points is high risk.
A typical example: a 65W charger with wireless charging function is high risk because it is connected to mains electricity, has high power, and has wireless function; an ordinary 20W USB-C charger is medium risk; while an ordinary 5V passive charging cable, with no active circuit and low power, is low risk.
Four Levels of Attributes and Seven Categories of Compliance Requirements
When sorting out compliance requirements, many people mix official regulations, platform requirements, and customer requirements together, leading to over-auditing or under-auditing. In fact, compliance requirements can be divided into four levels according to binding force from high to low:
The first level is statutory mandatory requirements, which are required by the laws of the target market and must be complied with; failure to comply is illegal. However, RoHS, FCC, etc. are statutory requirements only when the product meets the applicable conditions of the corresponding regulations; you should first determine the product scope, exclusions, and authorization procedures, and then verify all applicable obligations.
The second level is default channel/market requirements, which are not legally mandatory, but must be met if you want to enter this channel. For example, UL test reports required by Amazon and BSCI audits required by offline supermarkets — you cannot list products without them.
The third level is contract/customer custom requirements, which are additional requirements agreed upon by your customer or in the contract. For example, if a customer requires an additional environmental test, this shall follow the contract.
The fourth level is internal risk control requirements, which are additional requirements added by your own company to reduce risks. For example, requiring suppliers to provide a record of no violations in the past 3 years — this can be adjusted according to your own risk preference.
The corresponding compliance categories mainly cover seven major areas: product safety, EMC/radio frequency, environmental protection and chemicals, energy efficiency, consumer rights and product liability, trade and transportation. When auditing, follow the logic of “first verify statutory mandatory requirements, then add channel, customer, and internal additional requirements”, don’t check everything at once.
Corresponding Rules for Responsible Entities and Requirement Levels
Regulatory audits are not the responsibility of a single department. Different items correspond to different responsible departments: the procurement department is responsible for qualification and commercial audits, the regulatory department is responsible for determining access certifications and standards, and the quality department is responsible for process and material control. Clear division of labor ensures no items are missed.
To avoid over-auditing, all audit items should preferably be marked according to the four levels: [Statutory Mandatory], [Channel Requirement], [Contract Requirement], [Internal Risk Control], with priority from high to low. When the budget is limited, low-priority items can be put aside first.
If you are a beginner who does not know where to find authoritative regulatory information, do not randomly search online posts or listen only to the supplier’s side. Prioritize checking two places: one is the official website of the regulatory authority of the target market, such as EUR-Lex of the EU and CPSC (Consumer Product Safety Commission) of the US; the other is the compliance center of the sales platform you use — the platform’s requirements are well-organized and more targeted.
Core Audit Item Checklist (Exclusive for Charging Products)
After building the framework, you can enter the specific audit process. The checklist below is divided by modules, and each item is marked with the corresponding requirement level. You can add or delete items according to your own situation.
I. Supplier Entity and Business Qualification Audit
This part is the foundation of the audit. First confirm that the supplier itself is legal and compliant, then check product issues.
1. Basic Business Qualification Verification [Statutory Mandatory + Internal Risk Control]
The first thing to check is the supplier’s basic business qualifications, including business license or commercial registration certificate. It is necessary to verify whether the supplier’s local registration, license, and actual business qualifications cover relevant activities; the specific wording of the business scope may not list “charging products” item by item, and whether a specific production license is required also depends on the laws of the supplier’s location.
It is also necessary to confirm the production entity and address information. Verify the manufacturer, production location, applicant, and authorization relationship listed in the certification documents, and explain any address differences between quotations, certificates, and contracts, rather than uniformly requiring the addresses on all documents to be exactly the same. Many suppliers use certificates from other factories for affiliation. If the relationship between these entities and addresses cannot be explained, the subsequent certification documents may not be able to prove the compliance of the actually purchased products.
Import and export capabilities are also indispensable: the supplier must have independent import and export rights, or a compliant customs broker, that can provide formal customs declaration forms and origin documents, otherwise there will be problems during customs clearance.
Finally, there must be a dedicated compliance contact who can respond to your compliance questions in a timely manner. Otherwise, if a problem occurs, you cannot find the right person, which will delay matters.
2. Subcontracting and Supply Chain Transparency [Contract Requirement + Internal Risk Control]
Many suppliers do not do all processes by themselves and outsource part of them. This requires checking the subcontracting situation to avoid black-box operations.
Suppliers should be required to disclose whether key processes such as wire processing, PCB soldering, and shell injection molding are outsourced. If they are outsourced, you need to know who they are outsourced to and whether they have corresponding qualifications.
The source of core components must also be traceable: for core components such as charger transformers, USB-C interfaces, and wire core materials, the supplier and relevant certifications must be traceable. Otherwise, the root cause cannot be found when problems occur.
A change notification mechanism should also be agreed in the contract: if the supplier changes the production address or key subcontractors, it must notify you in writing in advance. Otherwise, if the factory is secretly changed, the previous audit will be in vain.
3. Dishonesty and Risk Screening [Internal Risk Control]
It is also necessary to check whether the supplier has any dishonesty or violation records to avoid pitfalls. There are three main verification channels: the dishonesty list of the target market’s customs, international sanctions lists such as the US SDN list, and enterprise credit publicity platforms.
During verification, record the date and scope of the query, and confirm that the supplier is not included in the blacklist or dishonesty list.
Also check historical violation records, such as major product recalls, environmental penalties, and labor violation records in the past 2 years. This standard can be set by yourself; for example, some enterprises require 3 years, some require 2 years.
II. Product Access Compliance Audit [Statutory Mandatory + Channel Requirement] (Core Must-Check)
This part is the core of the audit, which directly determines whether the product can legally enter the target market, and must be 100% verified.
Statutory Access Requirements by Market
Access requirements vary greatly across different countries and regions. I have sorted out the core requirements of major target markets, and you can check against them:
| Target Market | Core Mandatory Compliance Requirements | Main Applicable Products | Responsible Entity | Common Exceptions |
| EU | Low Voltage Directive (LVD), Electromagnetic Compatibility/Radio Equipment Directive (EMC/RED), Restriction of Hazardous Substances Directive (RoHS), relevant obligations under the Registration, Evaluation, Authorization and Restriction of Chemicals (REACH), ecodesign requirements for energy-related products, Waste Electrical and Electronic Equipment Directive (WEEE), packaging Extended Producer Responsibility (EPR), common charger rules (determined according to applicable product categories and conditions) | Electrical equipment with AC 50-1000V/DC 75-1500V, products within the scope of EMC or RED, electrical and electronic equipment within the scope of RoHS, applicable energy-related products and responsible entities | Importer/responsible person within the EU | Passive cables are usually not subject to LVD or ErP; specific determination shall be made based on product scope, exclusions, and regulatory conditions |
| US | FCC Part 15 related equipment authorization requirements, federal external power supply energy efficiency requirements (when applicable), California Proposition 65 (material risk) | Products containing digital circuits or wireless functions subject to Part 15, products within the scope of federal external power supply regulations | Specific responsible entities such as US importers/manufacturers | Ordinary passive cables usually do not independently trigger FCC equipment authorization; products not within the scope of external power supplies are not subject to DoE external power supply requirements |
| Japan | Systems and markings corresponding to product categories under the Electrical Appliance and Material Safety Law (PSE) | Electrical products designated by the Electrical Appliance and Material Safety Law | Japanese importer/producer | Ordinary USB cables are usually not within the scope of PSE |
| UK | Whether CE or UKCA is used in the GB market shall be determined according to the corresponding UK regulations and current government recognition policies for the product; for Northern Ireland, CE/CE UKNI shall be determined according to applicable EU rules | Electrical and electronic products sold to corresponding regions of the UK and within the scope of relevant UK or EU regulations | Responsible person/importer within the UK | The applicable rules for GB and Northern Ireland are different, and shall be determined separately according to the sales region and product regulations |
| Australia | Registration, declaration, test evidence, and marking requirements shall be determined according to EMC, radio, and electrical safety rules applicable to RCM and EESS product classes | Mains-input electrical equipment or electrical equipment within relevant regulatory categories | Domestic supplier/importer in Australia | Whether low-voltage passive products trigger relevant requirements shall be determined according to specific product categories and state/territory rules |
| South Korea | Mandatory systems such as safety certification, safety confirmation, and supplier’s declaration of conformity shall apply according to product categories, and corresponding KC markings and documents shall be verified | Products designated by the Electrical Appliance Safety Act | South Korean importer/manufacturer | The system for low-voltage passive products still needs to be specifically determined according to the Korean statutory product catalog, and cannot be uniformly regarded as voluntary |
Note: Whether CE can be used, whether UKCA is used, and the validity period for the UK GB market must be determined according to the corresponding UK regulations and current government recognition policies for the product; for Northern Ireland, CE/CE UKNI shall be determined according to applicable EU rules.
In the EU market, LVD applies to electrical equipment with AC 50-1000V or DC 75-1500V that falls within its scope. For EMC, it should first be determined whether the product is equipment subject to the EMC Directive; “whether it has a circuit” cannot be simply used as the only condition. When RED applies to radio equipment, technical documentation, testing, or other conformity assessments shall be completed according to its conformity assessment procedures and an EU DoC shall be signed. A so-called “RED report” in a unified format cannot be generally required.
RoHS applies to electrical and electronic equipment within its defined scope, and is affected by the exclusions and annex exemptions of the directive; it shall be determined item by item according to product category, use, and substance exemptions. REACH is not just about checking the “restriction” part by material; it is also necessary to verify REACH restricted substances, SVHC information transfer, and other applicable obligations according to products and materials. For finished products, special attention should be paid to the possible information transfer obligation when the concentration of SVHC in articles exceeds 0.1% (by weight).
If the product is an applicable energy-related product such as an external power supply, the energy efficiency indicators, technical documentation, and conformity declaration of the applicable ecodesign regulations shall be verified; do not generally require all products to provide an “ErP test report” and “energy efficiency label”. WEEE recycling marking and registration, as well as packaging EPR registration, declaration, recycling, and marking, shall also be specifically determined according to the product, sales member state, and responsible entity. There is no “packaging recycling mark” requirement uniformly applicable to all packaging in the EU.
The common charger rules cannot be applied mechanically. During the audit, first determine whether the product belongs to the equipment category specified in the annex of the Radio Equipment Directive, whether it supports wired charging, and the sales date; only when these conditions are met shall the relevant requirements for common chargers, USB-C charging interfaces, and USB PD be verified. A universal wall charger sold separately cannot be deemed to necessarily fall within this special scope just because it uses a USB-C interface or reaches 65W.
In the US market, first determine whether the product contains digital circuits or wireless transmission functions subject to FCC Part 15. When applicable, corresponding authorization procedures such as SDoC (Supplier’s Declaration of Conformity) or FCC certification shall be completed according to the specific equipment category. Ordinary passive cables usually do not independently trigger FCC equipment authorization, but this cannot be extended to all cable assemblies or products with electronic components.
If the product falls within the scope of US federal external power supply regulations, the minimum energy efficiency, no-load power consumption, test records, and nameplate or marking requirements shall be verified according to 10 CFR Part 430 and applicable standards; otherwise, the DoE external power supply requirements do not apply. California Proposition 65 shall be determined based on product materials and exposure risks.
For the Japanese market, first determine the product category according to the catalog of the Electrical Appliance and Material Safety Law. If it belongs to specified electrical appliances and materials, third-party conformity inspection, declaration, and diamond PSE shall be verified; if it belongs to other designated appliances and materials, the corresponding declaration, technical requirements, and circular PSE shall be verified. PSE is not a “certification document” that is the same for all designated products; responsibilities and documents vary by product category.
For the Australian market, the responsible supplier, registration, declaration of conformity, test evidence, and marking requirements shall be determined according to EMC, radio, and electrical safety rules applicable to RCM and EESS product classes. Not all products require the same set of “accredited laboratory reports, declaration of conformity, and EESS registration.”
For the South Korean market, it shall be determined according to the statutory product catalog whether it belongs to mandatory systems such as safety certification, safety confirmation, or supplier’s declaration of conformity, and the corresponding KC markings and documents shall be verified. The supplier’s declaration of conformity cannot be generalized as a voluntary category.
Interface Special Items (Channel/Industry Requirements)
In addition to statutory requirements, there are also some interface-related industry or channel requirements. Although they are not legally mandatory, they may need to be verified when customers, platforms, or products claim to use relevant certification marks.
USB-IF certification and mark authorization are voluntary industry or commercial requirements. Only when required by customers or platforms, or when the product claims to use USB-IF related certification marks, shall its certification status and authorization scope be verified. It cannot be regarded as a universal necessary condition for all USB-C PD chargers or charging cables.
For Lightning accessories, if they use Apple-related trademarks, certification marks, or require specific compatibility capabilities, MFi authorization and applicable contract requirements shall be verified. MFi is an Apple authorization program, not a universal statutory access condition for all Lightning cable sales platforms; the absence of MFi does not absolutely mean that the product will definitely not be recognized or cannot charge.
Technical Document Consistency Verification
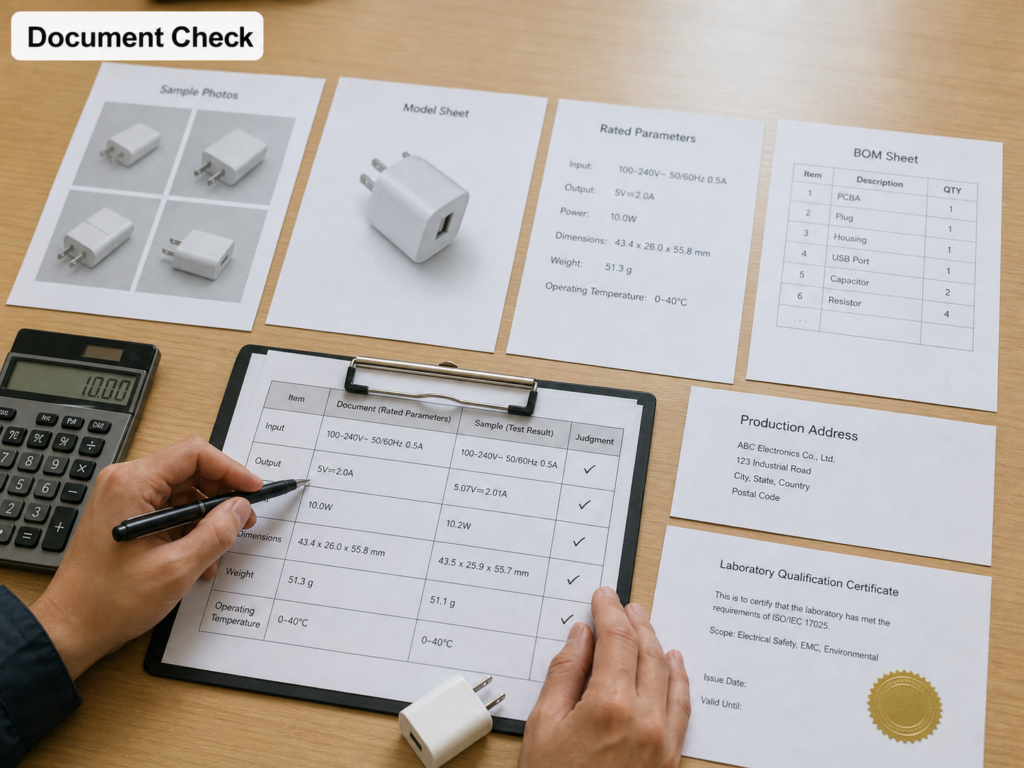
Many people only look at the cover when checking certifications, which is a big mistake. Even if the certificate is real, if it does not match the product you purchased, it is useless.
During verification, first confirm the minimum set of evidence packages, that is, the necessary documents: product model, rated parameters, sample photos, bill of materials (BOM), production address, and laboratory qualification. None can be missing.
Then is parameter consistency: the product model you purchased, input/output voltage/power, and cable current rating must be completely consistent with those on the test report. For example, if you buy a 65W charger but the report says 20W, that is definitely not acceptable, even if the model differs by only one letter.
Also pay attention to the requirements for retesting after changes: if the product’s wireless function, fast charging protocol, number of ports, or key materials change, the corresponding items must be retested. You cannot muddle through with old reports. For example, if the original USB-A interface is changed to USB-C, relevant safety and compatibility items must be re-evaluated.
Label, Packaging, and Manual Compliance
Product labels, packaging, and manuals may seem like trivial matters, but many customs detentions and platform removals are due to non-compliant labels.
Product labels must have rated parameters, safety warnings, compliance marks, and country of origin in the language of the target market. For example, for products sold to the EU, the label must have the applicable CE mark, and the input and output parameters must be clearly written in the local language.
Packaging and environmental protection marks shall be marked with recyclable marks and plastic restriction requirements according to the requirements of the target market. Packaging EPR, registration, declaration, and marking requirements shall be confirmed by specific member states and responsible entities, and cannot be generalized as a unified EU packaging recycling mark.
The manual must have correct usage instructions and safety warnings, and the language must meet the requirements of the target market; it cannot only be in Chinese.
What absolutely must not be done is falsely marking power, fast charging speed, interface version, or fraudulently using compliance marks. For example, marking CE without completing the applicable CE conformity assessment is a high-risk behavior, and may face regulatory measures if discovered.
III. Production and Continuous Compliance Capability Audit [Statutory Mandatory + Contract Requirement + Internal Risk Control]
A qualified product sample does not mean that mass-produced goods are qualified. This part is to check whether the supplier can consistently produce compliant products.
1. Material and Process Control
The compliance of core materials shall be classified by level: which are mandatory required by regulations, which are internally controlled by the supplier, and which are required by the purchaser’s contract. Do not confuse them. For example, hazardous substances required by RoHS are statutory mandatory, while the wear resistance test of wires is internally controlled by the supplier.
Mass production sampling inspection is indispensable: mains chargers shall implement the specified routine safety tests or sampling inspections according to applicable standards, certification schemes, and production quality plans, and keep records. The specific content, sampling ratio, and frequency of items such as withstand voltage, insulation resistance, and ground continuity shall be subject to applicable product standards, certification schemes, quality control plans, and contracts. It shall not be generally stipulated that all products must adopt the same test items and frequency for each batch.
There must be a control process for non-conforming products: non-compliant products must have special isolation, treatment processes and records, and cannot be mixed into mass-produced goods for shipment. For example, chargers that fail the test must be stored separately, clearly marked, and either reworked or destroyed.
2. Environmental Protection and Chemical Management
In terms of hazardous substance control, suppliers shall provide RoHS and REACH conformity declarations to prove that the hazardous substances in the products meet the requirements. Specifically, restricted substances and SVHC information shall also be verified according to product scope, materials, and applicable obligations.
Hazardous chemical management must be in place: hazardous chemicals used in the production process, such as flux, cleaning agents, and inks, must have Safety Data Sheets (SDS) — documents that record chemical composition, hazards, and protection methods. And storage must meet local regulatory requirements, for example, stored in a ventilated place with fire prevention measures.
Hazardous waste disposal must be compliant: hazardous waste generated in the production process, such as waste ink and waste flux, shall be disposed of according to local laws, the type and quantity of waste generated. For example, a qualified hazardous waste disposal company must be found, and it cannot be dumped casually.
3. Basic Labor and Occupational Health Compliance [Statutory Mandatory (Local Labor Law) + Channel Requirement]
This part must first comply with local labor laws, which is statutory mandatory. Secondly, many offline supermarkets and large customers will have additional requirements.
Prohibition of child labor and forced labor is the bottom line: suppliers must have employee identity verification records, and cannot detain employee documents or collect deposits — these are all illegal.
Working hours and wages must comply with local labor laws, with complete wage and working hour records. Forced overtime without overtime pay is not allowed.
Basic occupational health protection must be provided: for welding, injection molding, and chemical operation positions, there must be basic protective measures, such as masks and goggles, and fire-fighting facilities must be complete, meeting local safety requirements.
In terms of channel supplementary requirements, channels may require amfori BSCI audits, or social responsibility audits such as SMETA conducted through the Sedex platform. These are customer or channel audit requirements, not statutory product compliance certificates. If relevant requirements are not met, it may be impossible to enter specific offline channels or large customer systems.
4. Supply Chain Due Diligence [Statutory Mandatory (Specific Entities) + Contract Requirement + Internal Risk Control]
Supply chain due diligence has received increasing attention in recent years, but not all enterprises have statutory obligations, so do not over-audit.
Statutory obligations have boundaries: only specific entities that meet revenue or scale thresholds have statutory obligations, such as large EU importers and US listed companies. Small and medium-sized sellers generally do not have mandatory statutory obligations, and more are customer or internal risk control requirements.
Requirements for conflict minerals (3TG: tin, tantalum, tungsten, gold) shall be differentiated: for example, US listed companies have disclosure obligations, and EU conflict mineral regulations only require importers that meet the threshold, not all enterprises.
Traceability of high-risk raw materials is mostly non-mandatory: the source traceability of high-risk raw materials such as cobalt, lithium, and copper is mostly a customer or internal risk control requirement, and is only legally applicable in specific scenarios. There is no need to force suppliers to provide full-chain traceability.
The general boundary is: supply chain due diligence only needs to be done within a reasonable range. Do not over-promise 100% compliance across the entire chain — this is unrealistic and unnecessary.
IV. Trade and Cross-Border Transportation Compliance Audit [Statutory Mandatory + Logistics Requirement]
Even if the product is compliant, there must be no problems in transportation and customs clearance, otherwise it still cannot reach the destination.
1. Origin and Customs Classification
Origin determination and certification shall be differentiated by use: the requirements for origin documents for customs declaration and non-preferential origin are different. For example, a preferential certificate of origin is required to enjoy tariff preferences, while an ordinary origin declaration is sufficient for general customs clearance.
Customs code (HS code) classification must be accurate: for chargers, cables, and products with batteries, the HS code must match the function and structure of the product. Different codes correspond to different tariffs and regulatory requirements. For example, the code of a wireless charger with a battery is different from that of an ordinary wall charger. Incorrect classification may lead to customs detention and tax supplementation.
Commercial documents must be consistent: product information, quantity, and amount on invoices, packing lists, contracts, and origin documents must be consistent and cannot contradict each other. Otherwise, they will be suspected of fraud during customs clearance.
2. Import and Export Control and Intellectual Property Rights
Export control screening is indispensable: verification shall be conducted according to the product’s technical parameters, destination, end user, transaction party, and sanctions list. For example, some countries are sanctioned and products cannot be sold there; some products are subject to export control and cannot be exported casually.
Intellectual property rights must be compliant: products must have relevant patent authorizations for USB interfaces, fast charging protocols, etc. There must be no trademark or design infringement. For example, you cannot print Apple’s Logo casually or use others’ patented technologies, otherwise you will be sued.
OEM/ODM must have authorization: if it is private label production, there must be complete brand authorization documents proving that you have the right to let the supplier produce products of this brand. Otherwise, it will be deemed as counterfeit goods.
3. Transportation Compliance (Differentiated by Product Type)
Different products have different transportation requirements, which shall be verified accordingly. For ordinary charging products such as wall chargers and ordinary charging cables, it is sufficient that the transportation documents are complete and the packaging meets general transportation requirements.
For charging products containing lithium batteries, such as power banks and wireless chargers with batteries, the UN38.3 test report (mandatory test for lithium battery transportation by the United Nations) and dangerous goods declaration documents must be verified. Otherwise, they cannot be transported, especially by air, which has stricter requirements.
Different transportation channels have different requirements, and the restrictions for air freight, sea freight, and express delivery are different. Verification shall be conducted according to the transportation method you choose.
Dual-Product Audit Example (Comparative Reference)
Many beginners tend to mechanically apply audit standards and check all products according to the same requirements. Here, two typical products are compared to help you understand.
Example 1: 65W USB-C Wall Charger (High Risk, Mains Input)
This is a typical high-risk product, and a full check is required during the audit:
For the EU, first verify whether the product falls within the scope of regulations such as LVD and EMC, and prepare corresponding technical documentation, testing or other conformity assessments, EU DoC, and applicable marks according to the specific product and conformity assessment path; at the same time, verify relevant obligations under RoHS and REACH. If the product is an applicable energy-related product, the energy efficiency indicators, technical documentation, and conformity declaration of the ecodesign regulations shall be verified, and an ErP energy efficiency label shall not be generally required. Requirements such as WEEE and packaging EPR shall also be confirmed according to the sales member state and responsible entity. For the common charger rules, first determine whether the wall charger belongs to the radio equipment category specified in the rules. It cannot be deemed necessarily applicable just because it is USB-C or 65W.
For the US, first determine whether the product contains digital circuits or wireless transmission functions subject to Part 15. When applicable, complete corresponding authorization procedures such as SDoC or FCC certification according to the specific equipment category; if the product falls within the scope of federal external power supply regulations, then verify energy efficiency, no-load power consumption, test records, and marking requirements according to 10 CFR Part 430 and applicable standards. California Proposition 65 is determined based on material risk, and UL/ETL reports required by the channel shall also be checked.
For Japan, first determine the product category according to the catalog of the Electrical Appliance and Material Safety Law. If it belongs to specified electrical appliances and materials, third-party conformity inspection, declaration, and diamond PSE shall be verified; if it belongs to other designated appliances and materials, the corresponding declaration, technical requirements, and circular PSE shall be verified.
Example 2: Passive USB-C Data Cable (Low Risk, No Active Circuit)
This is a low-risk product, and there is no need to check those requirements for active products:
For the EU, verify whether the product falls within the scope of RoHS, and determine according to product category, use, exclusions, and substance exemptions; at the same time, verify applicable obligations such as REACH restricted substances and SVHC information transfer according to materials. Packaging EPR and marking requirements shall be confirmed according to the sales member state and responsible entity. There is no need to mechanically apply requirements for specific electrical equipment or energy-related products such as LVD and ErP.
For the US, it usually does not independently trigger FCC equipment authorization. California Proposition 65 is determined based on material risk, and there is no need to check DoE external power supply energy efficiency requirements.
General note: Never mechanically apply the withstand voltage, energy efficiency, and safety certification standards of wall chargers to check passive cables. This not only wastes time and cost, but also makes a fool of yourself.
Audit Implementation Process and Result Determination
With a checklist, you also need to know how to implement it step by step and how to judge the results. Otherwise, it is just empty talk.
Four-Step Audit Implementation Process
A formal audit is divided into four stages, which shall be carried out in order without skipping steps.
Stage 1: Self-Assessment and Document Collection
First, send a customized audit questionnaire to the supplier, which shall be adjusted according to your target market and product type. Do not send the same questionnaire to all suppliers. For example, the questionnaire for cable sellers is different from that for charger sellers, and the one for EU sales is different from that for US sales.
Then require the supplier to provide corresponding materials such as qualifications, certification reports, and production records. Also, have the supplier sign a commitment to the authenticity of information, clarifying that if information is concealed or falsified, corresponding responsibilities shall be borne, so as to increase the supplier’s cost of fraud.
Stage 2: Cross-Verification of Documents
After receiving the materials, do not trust them directly; conduct cross-verification. First, compare whether the information on the documents such as company name, address, product model, standard version, and issuing authority is consistent. For example, if the company name on the business license is different from that on the certification certificate, further verify the applicant, manufacturer, production location, and authorization relationship. You cannot draw a conclusion directly just based on the different names.
Then verify the authenticity of the documents through the official website of the issuing authority and the laboratory qualification platform. Many certification certificates can be queried by entering the number on the official website, and fake certificates will be exposed immediately upon checking.
Also use samples, product photos, and specifications to verify whether the documents match the actual product. For example, the product in the report is white with two USB-C ports, but the sample you received is black with only one port — that is definitely wrong.
Stage 3: On-site/Remote Verification (Selected as Needed)
Whether to conduct an on-site audit depends on your order scale and product risk. If it is a high-risk supplier or a large order, it is best to conduct an on-site audit to see if the production workshop, warehouse, and finished product labels are the same as stated in the documents.
For small and medium-sized orders or long-term cooperative suppliers, remote audits can be conducted via video connection to spot-check key processes and records, saving costs. When necessary, a third-party compliance agency can also be entrusted to conduct an independent audit, which is more objective and professional.
Stage 4: Risk Classification and Decision-Making
After the audit, classify the problems according to their severity, form a written audit report listing the found problems, risk levels, and rectification requirements, and then make corresponding decisions.
Risk Classification and Decision Rules (Adjustable as Needed)
Generally, problems are divided into three levels: red, yellow, and green, corresponding to different decisions:
• Red light (high risk, priority to eliminate/suspend cooperation): for example, forged documents, inability to prove compliance with statutory mandatory requirements, and major safety defects. These problems must never be touched. No matter how low the price is, you cannot cooperate, otherwise the loss will be huge when problems occur.
• Yellow light (medium risk, rectification within a time limit): for example, non-core items have defects that do not affect overall compliance, such as slightly smaller label font or a missing warning sentence in the manual. In this case, you can give the supplier a rectification period, and cooperate after the verification is passed.
• Green light (low risk, qualified): all statutory mandatory items are met, and there are no or only very minor problems in general items. In this case, normal cooperation can be carried out.
This classification is not fixed. You can adjust it according to the order scale, verifiability of rectification, local laws, and your own risk preference. For example, if the order amount is very large, yellow light items should also be stricter; if the order is very small, some non-core problems can be appropriately relaxed.
Evidence Determination and Rectification Closed Loop
During the audit, different evidences have different credibility. Ranked from high to low: official public records (such as customs credit records, regulatory authority announcements) > third-party authoritative institution reports (such as UL and TUV test reports) > supplier formal declaration + supporting records (such as RoHS declaration + raw material test report) > supplier oral promise (basically not counted).
If non-conformities are found, the record shall be clearly written: corresponding requirement, fact description, risk level, responsible person, rectification period, verification evidence, and closing date. It cannot be vague.
Rectification must form a closed loop. Suppliers are required to provide verifiable evidence, not just verbally say that it has been changed. For example, if the label is wrong, new label photos must be provided, and spot checks must be conducted to see if all mass-produced goods have been replaced. Otherwise, it is equivalent to no change.
One-Page Reusable Audit Form Template
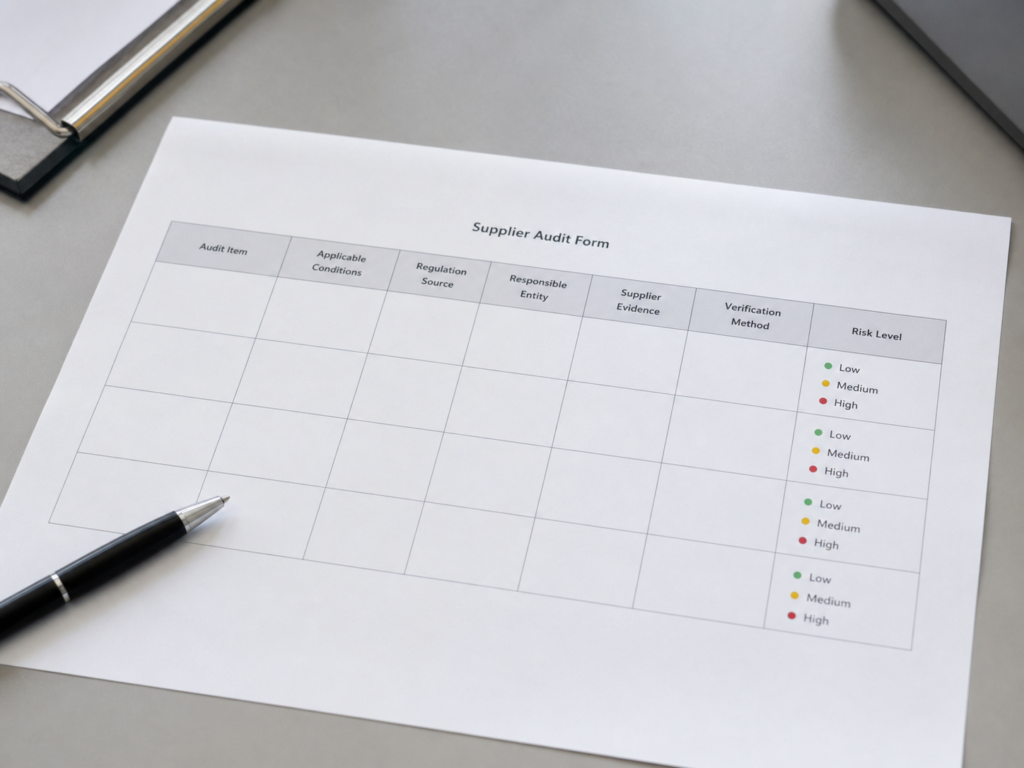
You can make a one-page audit form template for repeated use. The core fields include: audit item, applicable conditions, source of regulation/requirement, responsible entity, evidence provided by the supplier, verification method of the purchaser, and risk level.
When using it, you can add or delete items according to your product, market, and cooperation mode, without applying all items. For example, for low-risk products, you can delete some items that only need to be checked for high-risk products.
Risk-Based Checklist Simplification and Continuous Monitoring
Regulatory audits are not the stricter the better. It is necessary to balance cost and risk, and adjust flexibly according to different stages, different products, and different channels.
Adjust Audit Scope According to Procurement Stage
Different procurement stages have different audit focuses: in the sampling/inquiry stage, suppliers are still being screened, so a full audit is not needed. Only check core mandatory compliance documents and sample test reports, quickly screen out obviously unqualified suppliers, and reduce upfront costs.
Before bulk procurement, all applicable items must be fully audited, and core items must be 100% verified. After all, bulk procurement involves a large amount, and the loss is large if problems occur, so this money cannot be saved.
For long-term cooperative suppliers in the reorder/repurchase stage, there is no need for a full audit every time. Only spot-check the validity of documents, batch sampling records, and the completion of the last rectification, saving time and cost.
Adjust Audit Intensity According to Product Risk Level
Products with different risk levels have different audit intensities: for high-risk products such as 65W chargers with wireless charging function, it is necessary to strictly check safety compliance, production sampling records, material traceability, and energy efficiency compliance to ensure everything is foolproof.
For medium-risk products such as ordinary 20W chargers, just focus on interface certification, environmental compliance, and the authenticity of label parameters.
For low-risk products such as ordinary passive charging cables, it is sufficient to only check mandatory compliance documents, basic business qualifications, and label compliance.
Adjust Audit Focus According to Sales Channel
Different sales channels have different requirements, so targeted checks are needed: for e-commerce platforms such as Amazon and AliExpress, additional verification of special certifications, energy efficiency labels, and EPR registration numbers required by the platform is needed, otherwise products cannot be listed.
For independent stations, focus on verifying official regulatory requirements and consumer rights protection rules, according to the requirements of the sales country. For example, the EU consumer protection law requires 14-day no-reason return, so it is necessary to confirm that the supplier’s products meet relevant safety requirements to avoid return disputes.
For offline supermarkets such as Walmart and Carrefour, additional checks are needed for social responsibility audits required by the channel, such as amfori BSCI audits, or SMETA audits conducted through the Sedex platform, as well as product liability insurance. These are hard requirements for offline channels.
Continuous Compliance Monitoring Rules (General for the Whole Process)
An audit is not a one-time thing. Continuous monitoring is required, because regulations will be updated and suppliers will also change.
Periodic trigger: determine the audit frequency according to the product risk level and cooperation depth. For high-risk or core suppliers, once every six months to one year; for medium and low-risk suppliers, it can be appropriately extended, for example, once every 2-3 years.
Change trigger: if the supplier changes the production address, key materials, product model, or subcontractor, the corresponding items must be re-audited. For example, if the supplier of the USB-C interface is changed, the interface certification must be re-checked.
Regulatory update trigger: when new regulations come into effect, promptly require suppliers to provide updated compliance certificates. For example, after the EU common charger rules take effect for relevant products, it is necessary to confirm whether the supplier’s products meet the applicable requirements.
Incident trigger: if compliance incidents such as consumer complaints, product recalls, or customs detentions occur, a comprehensive re-audit shall be launched to see if there are other hidden problems.
Archive preservation: for all audit documents and records, the retention period shall be determined according to target market regulations, contracts, and company policies. For example, if some regulations require 5 years of retention, they must be stored for at least 5 years for regulatory inspection.
Common Audit Misconceptions and Pitfall Avoidance Guide
Many people tend to fall into some low-level pitfalls when conducting audits, which not only waste money but also have no effect. Here are 7 most common misconceptions to help you avoid pitfalls.
Misconception 1: Having a CE/certification mark equals full compliance
This is the most common pitfall. Many people think that a product with a CE mark is compliant. In fact, CE is just a compliance mark, not a single certification. EU CE usually involves the manufacturer’s declaration of conformity with applicable regulations and corresponding conformity assessment. Seeing the mark does not prove that all obligations have been completed. It is also common that certificates have expired standards, mismatched models, or even are affiliated or forged.
Pitfall avoidance method: don’t just look at the mark. Verify the assessment documents of the corresponding directives, declaration of conformity (DoC), standard version, and product matching. Also verify the authenticity on the official website of the issuing authority to confirm that the certificate is real and matches the product you purchased.
Misconception 2: Domestic compliance = global universal
Many people take it for granted that since their products sell well in their home country with domestic certification, they will be fine when sold to other countries. As a result, they only find out after the goods are detained by customs that regulations vary from country to country. For example, China’s 3C certification is not recognized by the EU or the US.
Pitfall avoidance method: first confirm the specific requirements of the target market according to the applicability determination factors we mentioned earlier, and then conduct the corresponding audit. Do not take it for granted to apply domestic standards.
Misconception 3: One audit is valid for life
Some suppliers will say “we passed the audit a few years ago” and then give you old reports. This is also a pitfall, because regulations will be updated, and suppliers may also change materials, move factories, or change subcontractors. Compliance a few years ago does not mean compliance now.
Pitfall avoidance method: according to the trigger rules of continuous monitoring, conduct regular or irregular re-audits, especially when there are changes or regulatory updates, a re-audit must be conducted.
Misconception 4: Only check the certificate cover, not the details
Many people only look at the logo and validity period on the cover of the certificate when checking certifications, and never read the content inside. As a result, the product model, power, and number of ports on the certificate are different from the actually purchased ones. For example, the supplier uses a 65W certificate for a 20W product, or the model differs by one letter, which is not the same product at all.
Pitfall avoidance method: be sure to check the product photos, parameters, and BOM list of the test report page by page to confirm that they are completely consistent with the product you purchased. Don’t be afraid of trouble.
Misconception 5: Only check traders, not the actual production entity
If your supplier is a trader, many people only check the trader’s qualifications and trust the certificates provided by the trader. This is also a big problem, because traders do not produce by themselves, and are likely to use certificates from other factories. They have no compliance control ability at all, and mass-produced goods are prone to problems.
Pitfall avoidance method: be sure to verify the qualifications and records of the actual production factory. Traders must provide factory authorization documents to prove that they are indeed cooperating with this factory.
Misconception 6: Only look at official regulations, ignore channel requirements
Many people think that as long as they meet the official statutory requirements, it is fine. As a result, even with mandatory certification, products are still removed from the platform, because the platform has additional requirements, such as the energy efficiency label registration number and UL test report required by Amazon. These are not statutory, but you must have them if you want to sell on the platform.
Pitfall avoidance method: before the audit, sort out the additional requirements of the sales channel you want to enter, add them to the audit checklist, and don’t just look at official regulations.
Misconception 7: System certification equals product compliance
Many suppliers will use system certifications such as ISO9001 and BSCI to prove product compliance, saying “we have ISO9001, so the product quality is fine”. In fact, these are two different things. System certification only shows that the factory has a management system, and does not mean that specific products meet safety and environmental protection requirements. amfori BSCI audits and SMETA audits conducted through the Sedex platform also belong to customer or channel social responsibility audits, and cannot replace product safety and environmental compliance certificates.
Pitfall avoidance method: be sure to distinguish between system certification, social responsibility audit, and product certification. For product access, the mandatory compliance documents of the corresponding product must be verified. Management system or social responsibility audits can only be used as a reference and cannot be used as evidence of product compliance.
Summary
After reading this content, you should be able to quickly build a suitable regulatory audit checklist for charging product suppliers according to your target market and product type, independently complete basic compliance verification, determine risk levels, and make reasonable cooperation decisions. You can also flexibly adjust the audit intensity according to the procurement stage, product risk, and sales channel, balance cost and risk, avoid common certification fraud and compliance blind spots, and reduce compliance risks in cross-border procurement. If you are a beginner, you can directly use the one-page audit template mentioned in the article, add or delete items according to your own needs, and quickly implement supplier onboarding and continuous monitoring.