Sellers operating in the U.S. market have almost all heard of “FCC certification” — either they are required to provide it during customs clearance, or their listings get blocked on Amazon or Walmart. Many people’s first reaction is “I have that certificate”, but they still get rejected. In fact, what the FCC requires is never a single certificate, but a complete set of documents proving that the product complies with electromagnetic interference and wireless transmission rules. Missing any one of them may result in a non-compliance ruling.
First, Understand the Basics: What FCC Documents Are, and Which Products Need to Prepare Them
The Core Role of FCC Documents Goes Far Beyond a Single Certificate
FCC is the abbreviation of the Federal Communications Commission, the official U.S. agency responsible for radio spectrum and electromagnetic interference, equivalent to the U.S. “Radio + Electromagnetic Compatibility Regulatory Bureau”. What we often call “FCC documents” is not a single stamped certification certificate, but a complete set of materials proving that your product complies with U.S. electromagnetic interference and wireless transmission rules. The specific composition varies depending on the compliance path and applicable equipment rules.
Its role is mainly reflected in three types of scenarios: First, during U.S. import customs clearance, customs may verify whether the compliance qualification matches the actual product based on product type and regulatory requirements. Missing core proof may lead to goods being detained. Second, it is an access requirement for listing on mainstream e-commerce platforms; missing it will result in delisting. Third, it serves as core evidence of compliance when encountering regulatory spot checks or consumer disputes. Generally speaking, a complete set of FCC documents roughly includes test reports, compliance declarations, technical documentation, labels and user manuals, and official authorization records. The specific composition varies significantly across different paths.
Which Category Does Your Product Belong To? Find Your Match First
Not all products require the same FCC documents. We can first make a basic classification based on the product’s emission characteristics, then correspond to the subsequent compliance requirements:
The first category is intentional radiators, that is, products that actively transmit wireless signals to achieve their functions — such as Bluetooth headsets, WiFi-enabled routers, remote control toys, mobile phones, smart door locks, etc. This category of products has the strictest compliance requirements.
The second category is unintentional radiators. These products do not intend to transmit wireless signals themselves, but because they contain digital circuits and switching power supplies, they inevitably leak some electromagnetic interference during operation, which may affect the normal operation of other devices. Examples include ordinary desktop computers, LED lights, mobile phone chargers, monitors, and wired keyboards and mice. Basically, all products with digital circuits but no wireless function fall into this category.
The third category is products subject to exemption rules, that is, equipment that meets the exemption conditions explicitly listed by the FCC, which do not require testing or authorization application. Many people think that only purely mechanical, completely non-electrical products are exempt. In fact, some specific low-emission, low-voltage devices may also meet exemption requirements. The specific situation must be judged against the current FCC rules, and there is no general rule that “all purely mechanical products are uniformly exempt”.
3 Concepts Most Easily Confused by Beginners
Many people’s misunderstandings about the FCC come from confusing these three concepts. Figuring them out in advance can save a lot of detours:
First, test reports are not equivalent to FCC certification. A test report is only the test result of the sample you sent to the laboratory, proving that the sample meets the requirements under test conditions. But it is not an official authorization, and you cannot claim your product has FCC certification just with a test report.
Second, the FCC ID label is not equivalent to a complete compliance file. The ID is just the “identity mark” of a wireless product. If any of the underlying test reports, technical documentation, or compliance declarations are missing, it is still non-compliant.
Third, the SDoC declaration is not equivalent to an official certificate. SDoC stands for Supplier’s Declaration of Conformity. Simply put, it is a “compliance guarantee” issued by the responsible party itself, where the responsible party promises that the product meets the requirements. It is not a certificate issued by the FCC or an official agency. Don’t confuse them.
3 Most Common Beginner Misconceptions
In addition to conceptual confusion, beginners most often fall into these three pitfalls:
First misconception: All FCC documents must be submitted to the FCC official. In fact, only some materials under the FCC ID path need to be submitted for review. All documents under the SDoC path only need to be archived by the enterprise for future reference, and do not need to be actively submitted to the FCC; they only need to be provided during spot checks.
Second misconception: Having a certificate means everything is fine. What the FCC requires is a complete compliance file. If you only hold the authorization certificate but lack supporting documents such as technical documentation and test reports, you will still be judged non-compliant in a spot check.
Third misconception: If a certified wireless module is used, the whole device no longer needs to prepare documents. Module certification has clear usage conditions; when the conditions are not met, the certification is invalid, and the whole device still needs to supplement compliance materials. Module certification cannot be directly reused. For specific requirements, please refer to the special scenarios section later.
Choose the Right Compliance Path: Document Requirements Are Determined by the Path
Many people look for a checklist right away when preparing documents, but end up following the wrong path and wasting their effort. FCC document requirements completely follow the compliance path, and requirements for different paths are vastly different. So the first step is always to determine which path your product should take.
Core Differences Between the Three Types of Compliance Paths
There are three main types of FCC compliance paths, which we can quickly compare with a table:
| Compliance Path | Applicable Product Type | Official Review Required | Unique FCC ID Available | Document Handling Method |
|---|---|---|---|---|
| FCC ID Certification | Intentional radiators that require authorization per FCC rules | Requires review by an FCC-recognized TCB before submission to the FCC system; final authorization is subject to records in the FCC official database | Yes, publicly queryable on the FCC official website | Some technical documentation can apply for confidentiality; core public information is disclosed |
| SDoC (Supplier’s Declaration of Conformity) | Unintentional radiators that comply with rules | No prior official review required; the U.S. responsible party is solely responsible | No exclusive ID | The enterprise retains the full set of documents on its own, and provides them during spot checks |
| Subject to Exemption Rules | Products that meet FCC explicit exemption clauses | No review or testing required | No | Only need to retain materials proving compliance with exemption conditions |
Here is a brief explanation of TCB: It is a telecommunication certification body officially recognized by the FCC, responsible for reviewing Certification application materials in accordance with FCC established procedures, and submitting them to the FCC Equipment Authorization System after confirming compliance. It does not independently issue certificates on behalf of the FCC. The validity of the final equipment authorization is subject to the public records in the FCC official database.
Four-Step Quick Judgment Method, Get Results in 1 Minute
You can use four simple questions to quickly make a preliminary positioning of your product, though final confirmation still needs to be made against specific FCC rules:
First question: Does your product actively transmit wireless signals? For example, functions like Bluetooth, WiFi, cellular network, remote control, NFC? If yes, you need to first check against applicable FCC rules to confirm whether it belongs to the device type that requires Certification (FCC ID), and whether there are exemptions or other authorization methods. Most conventional consumer wireless products usually follow the FCC ID certification path.
If not, ask the second question: Does the product only have digital circuits or switching power supplies, with no wireless transmission function at all? For example, ordinary desk lamps, chargers, monitors, wired headsets? If yes, and it falls within the applicable scope of SDoC, follow the SDoC path.
If not, third question: Does the product meet the exemption scenarios explicitly listed by the FCC? If yes, just retain supporting materials as required by the exemption.
Finally, there is a supplementary question: Does your product use a wireless module that has already obtained FCC ID certification? If yes, some of the module’s materials can be reused when the module meets the usage conditions, but the whole device still needs to supplement its own compliance assessment. You cannot directly use the module’s certification as the whole device’s certification.
For composite digital products with wireless functions (such as WiFi-enabled smart monitors), there is no need to mechanically make two separate applications. Usually, the FCC ID path is the main one, but the application materials and test reports must simultaneously cover all applicable requirements such as wireless transmission, digital circuits, and EMC. If the reviewer judges that some requirements are not covered, corresponding test records or declaration documents still need to be supplemented. Having an FCC ID does not automatically cover all unintentional emission-related requirements.
These Special Situations Will Change Document Requirements
Some products have special situations and cannot directly apply the basic path, requiring additional supplementary documents:
The first type is wireless products used near the human body, such as smart watches, Bluetooth headsets, and VR headsets. These require additional radio frequency (RF) exposure assessment documents to prove that the product’s wireless radiation is safe for the human body. The specific assessment method (such as MPE, SAR, or other applicable methods) is jointly determined by the product’s transmission power, operating frequency, antenna characteristics, distance from the human body during use, simultaneous transmission status, and applicable FCC rules. It cannot be simply judged by “whether it is in contact with the skin”.
The second type is products with multiple frequency bands and multiple wireless functions, such as routers that support 2.4G WiFi, 5G WiFi, and Bluetooth at the same time. These require supplementary operating parameters for each frequency band, descriptions of different operating modes, and relevant test or assessment materials for combinations of multiple functions transmitting simultaneously.
The third type is software-upgradable products, which require supplementary descriptions of software control mechanisms to prove that the device will still not exceed the authorized operating parameter range after upgrade. This may specifically involve RF parameter locking, configuration permission management, version control records, and change assessment processes, not just requiring “locking transmission power and frequency band”.
Full Checklist of Required Documents for FCC ID Certification
FCC ID is the path with the strictest requirements and the most documents. If your product is an intentional radiator that requires Certification, prepare according to this checklist.
Category 1: Application Identity and Authorization Documents
These documents are the “stepping stone” for the application, proving that you are eligible to submit the application:
FCC Form 731 is the official FCC equipment authorization application form, equivalent to the “registration form” for your certification application. It requires filling in basic product information, applicant information, technical parameters, etc. The FCC Registration Number (FRN for short) is the unique identity number of the applicant in the FCC system, just like your “ID number” at the FCC. Without it, you cannot submit an application, and both enterprises and individuals must register first.
If you entrust an agency or TCB to submit the application on your behalf, you also need a Power of Attorney (POA for short) to prove that you entrust the other party to handle related matters. Finally, the complete information of the U.S. Agent must be provided: The FCC requires all foreign applicants to designate a U.S.-based contact entity, which is mainly responsible for receiving official FCC notifications and coordinating with regulatory inquiries. It does not directly bear all compliance responsibilities for the product, and corresponding authorization documents are required to prove the cooperative relationship.
Category 2: Product Technical Documentation (Including Confidentiality Rules)
These documents are used to prove what your product is and how it works. What everyone is most concerned about here is confidentiality — after all, many core technologies do not want to be disclosed.
The technical documentation to be prepared includes: basic identity information such as product name, model, software and hardware versions, functions and uses; circuit structure materials such as system block diagrams and circuit schematics; real photos of the product’s internal and external appearance, interfaces, and label positions; and core wireless parameters such as operating frequency band, modulation method, maximum transmission power, antenna type and gain.
Regarding confidentiality rules, FCC confidentiality applications must comply with 47 CFR Part 0 and the current rules of the Equipment Authorization System. Different types of materials have different confidentiality eligibility and term requirements, and the final result is subject to the approved application: Sensitive technical materials such as circuit schematics and core technical descriptions can usually apply for confidentiality, and the specific term (long-term/short-term) must be applied for in accordance with the rules; the confidentiality eligibility of materials such as internal photos and test setup photos must be judged in combination with the application scenario, and are not uniformly limited to short-term confidentiality; while end-user-oriented materials such as FCC ID labels and user manuals are usually not allowed to be kept confidential for a long time and must be disclosed on the FCC official website.
Category 3: Test and Compliance Assessment Reports
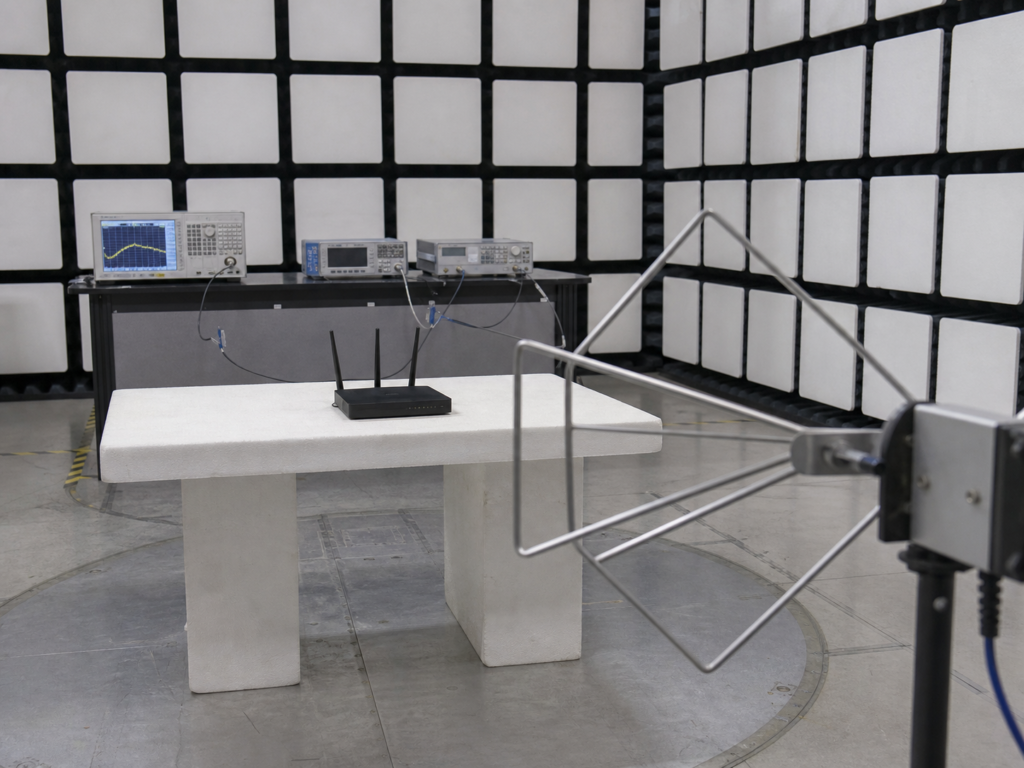
These documents are the core evidence proving that your product meets the standards. Test items must be determined according to the corresponding FCC Part rules, functions, frequency bands, and operating modes of the product. Not all wireless products uniformly undergo a set of RF + EMC tests. Test materials under the Certification path must be completed by a laboratory that meets FCC requirements. Common test items include transmission power, frequency bandwidth, conducted interference (interference transmitted through power lines), radiated interference (interference transmitted through air), etc. Test items vary for different products, but all must comply with the corresponding FCC rules.
Then there is the RF exposure assessment report, which is only required for wireless products used near the human body. The assessment method must be selected according to applicable rules in combination with factors such as transmission power, frequency, antenna, usage distance, and simultaneous transmission status: MPE (Maximum Permissible Exposure) assesses compliance by calculating safe distances and other methods; SAR (Specific Absorption Rate) assesses by testing the absorption of RF energy by human tissues. Other applicable assessment methods may also be used in some scenarios.
Finally, there are test supporting instructions, such as how the sample was placed during testing, what configuration was used for testing, and what antenna was used, to prove that the test process is standardized and the results are traceable.
Category 4: Labels and User Materials
These documents are for end users and must meet FCC labeling requirements:
First is the FCC ID label, which must be printed with the unique FCC ID number. You also need to submit the label design draft and its position diagram on the product. Labels for conventional devices must comply with FCC equipment authorization label rules and be placed in a position accessible to users without tools. If the product is extremely small (such as true wireless earbuds, small sensors) and there is no suitable housing position to paste the standard label, a simplified label can be applied for under the premise of complying with corresponding FCC rules. If the product has an electronic display interface, an electronic label (i.e., displaying the FCC ID in interfaces such as system settings) can be applied for when conditions are met. For some very small devices, the label can be placed on the packaging or in the manual, but this must meet specific FCC conditions and be confirmed by review, and cannot be adjusted independently.
Then is the user manual, which must include the FCC compliance declaration, interference warning statements required by corresponding rules (telling users that this product may cause interference to other devices), and relevant usage restrictions — such as not being able to randomly replace non-designated antennas, what the human body safety distance of the product is, and how users can adjust if interference occurs. The specific content must comply with applicable FCC Part rules.
Category 5: Official Documents That Must Be Retained After Approval
After the application is approved, you will receive the equipment authorization certificate (Grant for short) forwarded by the TCB, which is commonly known as the “FCC certificate”. It will clearly state information such as product model, FCC ID, complied rules, and issuance date. But it is important to note: The validity of the final authorization is subject to the public records in the FCC official website’s Equipment Authorization Database. Anyone can query and verify using the FCC ID. This is very important because both customs and e-commerce platforms will check the authorization information on the official website.
Required Documents for SDoC Declaration of Conformity
SDoC is the compliance path for unintentional radiators. Many people think that SDoC is just writing a declaration casually, but that’s not the case. It also requires a full set of archived documents, except that they do not need to be submitted to the official for review in advance.
Core Documents That the Responsible Party Must Archive
You don’t need to submit these documents to the FCC, but you must keep them well on your own, and be able to produce them during spot checks, customs clearance, or platform reviews:
The first is the formal SDoC declaration, issued by the U.S. Responsible Party that bears compliance responsibility. It must include the product model, complied FCC rule clauses, complete information of the U.S. Responsible Party, and the signature and seal of the Responsible Party — this is the core document of SDoC, equivalent to the Responsible Party’s “compliance guarantee”. Special attention should be paid here: The U.S. Responsible Party for SDoC is the entity that directly bears legal compliance responsibility, which is not the same role as the US Agent in FCC ID that is only responsible for liaison. Foreign enterprises cannot directly serve as the Responsible Party for SDoC, nor can they use ordinary agency authorization letters to replace legal responsibility documents.
The second is supporting test records/reports: The SDoC path has no official mandatory pre-requirements for laboratory qualifications. The Responsible Party must retain test materials that can fully prove the product complies with applicable FCC rules. Test items must be determined according to the corresponding FCC Part rules of the product. In practice, to meet the persuasiveness requirements of platform reviews, importer verification, and regulatory spot checks, laboratories with corresponding testing capabilities are usually selected to issue reports. Test records must never be fabricated. If falsehood is found in a spot check, the penalty will be very severe.
The third is product technical documentation, including product model specifications, function descriptions, and appearance photos, to prove that the product you tested is the same as the product you sell.
The fourth is relevant supporting documents of the U.S. Responsible Party, proving that this U.S.-based entity agrees to bear the SDoC legal compliance responsibility for this product.
Compliance Content Included with the Product
In addition to archived documents, the product itself must also meet corresponding labeling requirements:
SDoC products do not have an exclusive FCC ID. The FCC compliance mark on the product or packaging is optional and not mandatory. However, the user manual must include applicable FCC interference warning statements, and also tell users what mitigation measures they can take on their own if interference occurs — such as changing the socket, adjusting the antenna direction, moving the product further away from the interfered device. This part is a mandatory requirement.
Core Rules of SDoC
Finally, let’s emphasize two key rules of SDoC to avoid pitfalls:
First, SDoC does not need to be submitted to the FCC for official review, and is fully the responsibility of the U.S. Responsible Party. However, if document fraud or product non-compliance is found in a spot check, the penalty will be very severe, as it constitutes “false self-declaration”.
Second, SDoC only applies to unintentional radiators that comply with the rules. For products with wireless transmission functions, the wireless transmission part usually cannot complete compliance solely through SDoC, and must be judged according to corresponding FCC rules. Composite devices may involve different compliance requirements at the same time.
Additional Document Requirements for Special Scenarios
In addition to the two basic paths, there are some special scenarios that require additional supplementary documents. Don’t miss them.
Situation of Using Certified Wireless Modules
Many products use ready-made wireless modules that have obtained FCC ID certification. In this case, it should be clear that using a certified module does not mean that the whole device automatically obtains compliance authorization. Only when the module’s authorized usage conditions are fully met can part of the module’s certification materials be reused, without the need to retest the module itself.
Reusable module documents include: the module’s FCC ID Grant (authorization certificate), test report summary, and the module’s official integration guide (which will clearly state the module’s installation requirements, antenna restrictions, usage conditions, simultaneous transmission requirements, etc.).
Documents that the whole device needs to supplement include: instructions for using the module in the whole device, necessary supplementary tests or assessments (for example, if you replace the antenna with one not specified by the module, you need to supplement the radiated power test), and the whole device’s label and user manual — the whole device must clearly mark the FCC ID number of the module used, and cannot use the module’s ID as the whole device’s ID.
Special attention should be paid here: If the whole device design does not meet the requirements of the module integration guide (such as excessive antenna gain, insufficient installation distance, unsatisfactory shielding conditions, non-compliance of multiple transmitters working simultaneously, etc.), the module’s authorization cannot be extended to the whole device, and the whole device needs to re-apply for the corresponding FCC compliance authorization.
Situation of Near-Body/Wearable Wireless Devices
If your wireless product is used near the human body, such as smart bracelets, Bluetooth headsets, smart glasses, VR headsets, in addition to the conventional FCC ID documents, three additional types of documents are required:
- RF exposure assessment report. The specific assessment method must be determined according to applicable FCC rules in combination with the product’s transmission power, operating frequency, antenna characteristics, human body distance in usage scenarios, simultaneous working status of multiple transmitters, etc.;
- Description of the product’s actual usage scenarios, such as wearing position, average/minimum distance from the human body during normal use, common working modes, etc.;
- Usage restrictions in the user manual, such as correct wearing method, minimum human body safety distance, prohibited usage scenarios, etc. The specific content must be consistent with the assessment results.
Situation of Multi-Band/Software-Upgradable Devices
Products with multiple frequency bands and multiple wireless functions, such as routers that support both 2.4G and 5G WiFi, smart watches with both Bluetooth and cellular, need to supplement parameter tables for each frequency band, descriptions of each working mode, and test or assessment materials for combinations of multiple frequency bands/functions transmitting simultaneously, to ensure that all working states meet authorization requirements.
Software-upgradable products, such as smart devices that can update firmware via APP or USB flash drive, need to supplement descriptions of software control mechanisms to prove that the device will still not exceed the authorized RF parameter range after local or remote upgrade. This may specifically include RF parameter locking mechanisms, firmware configuration permission management, software version control records, compliance assessment processes for firmware changes, etc.
Required Documents for Products Subject to Exemption Rules
Many people think that exempt products don’t need to prepare anything, but that’s not the case. When a spot check occurs, you have to be able to prove that you meet the exemption conditions. Since FCC exemption clauses have different requirements for different devices, there is no unified “exemption path document checklist”. The core is to retain materials that can clearly explain that the product meets specific exemption clauses:
Common supporting materials include product specifications, Bill of Materials (BOM), function descriptions, written explanations of corresponding exemption clauses, etc. For example, a purely manual screwdriver can prove that it does not contain any electronic components through specifications + BOM, and complies with corresponding exemption rules. For other types of exempt products, corresponding materials must be prepared according to specific clauses.
Which Documents to Prepare for Different Scenarios
Many people ask: “Do I need to carry all documents with me?” Actually, no. The FCC documents that need to be provided in different scenarios depend on the product type, applicable rules, and specific requirements of the regulator or platform. There is no unified “must-carry document checklist”. The following are the conventional preparation directions for common scenarios. Just prepare as needed, so you won’t miss anything nor disclose core technology.
U.S. Customs Clearance
The routine verification direction in the customs clearance link is the matching degree between product compliance qualifications and the actual product. Usually, a full set of technical documentation will not be actively requested. Whether to request documents and which documents to request depend on the specific product, import batch, and regulatory requirements. Not all products must submit FCC documents for customs clearance:
- For products authorized with FCC ID, you can usually prepare a copy of the Grant and FCC ID query information for verification;
- For products under the SDoC path, you can usually prepare a copy of the SDoC declaration and test report summary, and provide the contact information of the U.S. Responsible Party when necessary;
- Note: The full set of technical documentation still needs to be retained as required. When encountering further customs verification, regulatory linkage, or importer supplementary document requirements, it must be able to be retrieved and provided in a timely manner.
E-Commerce Platform Listing
The review requirements of e-commerce platforms belong to the platform’s own rules, not FCC legal requirements. Moreover, requirements vary greatly across different platforms and different categories, and shall be subject to the latest category rules of the corresponding platform:
- Common requirements: Intentional radiators need to provide FCC ID and authorization records queryable on the FCC official website; unintentional radiators need to provide SDoC declaration and corresponding test reports;
- Some platforms may require submitting compliance documents in the backend, displaying FCC compliance marks or FCC ID on the product detail page, and marking U.S. Responsible Party information. Specific display requirements are subject to platform rules;
- Common rejection reasons: The model on the certificate does not match the sales model, the FCC ID has no valid authorization record on the official website, the product version in the test report is inconsistent with the sales version. These must be checked in advance.
Regulatory Spot Checks and After-Sales Disputes
If you encounter a spot check by the FCC or market supervision, the document submission deadline and the scope of documents to be submitted are subject to the formal notice issued by the regulatory authority, and there is no unified legal deadline. It is recommended for enterprises to manage archives according to the standard of “full set of documents can be retrieved within 3-5 working days” to avoid penalties or delisting due to untimely retrieval. However, this deadline is only an internal management recommendation and does not equal a legal requirement.
If it is an ordinary after-sales dispute, for example, a consumer says your product interferes with their other devices, you only need to provide core supporting documents (such as FCC ID Grant, SDoC declaration) plus a test report summary. You don’t need to hand over trade secrets such as circuit schematics and core technical parameters.
Here is a reminder: The accessibility of documents will directly affect the efficiency of problem handling — if you delay for a long time and still can’t produce the documents, even if you can produce them in the end, the product may have already been delisted or the goods detained. So be sure to sort and organize the documents well and store them in a place where they can be quickly accessed.
Production and Mass Production Archiving
Many people only pay attention to the documents during application and ignore them during mass production, which is also a big pitfall. During the mass production stage, you need to retain two types of documents:
- Consistency records between mass-produced products and test samples: For example, the models of key components (chips, antennas, power supplies), firmware versions, structural design, etc. It is necessary to ensure that the compliance-related configurations of mass-produced products are consistent with the samples sent for testing at that time, and cannot be changed randomly;
- Product change records: If you later change the antenna, change the chip, modify the housing, change the power supply, or modify compliance-related parameters in the firmware, as long as the change may affect compliance, it must be recorded. When necessary, tests must be re-conducted and compliance documents updated.
Pitfall Avoidance and Self-Check: Complete Compliance Inspection in 10 Minutes
Finally, we have sorted out the minefields that beginners most easily step into, as well as a self-check process that can be completed in 10 minutes, to help you find problems in advance and avoid issues only arising during customs clearance or listing.
5 Types of Minefields Most Easily Stepped Into by Beginners
The consequences of each type of minefield are very serious, and everyone must avoid them:
The first type is document fraud or misappropriation. For example, forging authorization certificates, misappropriating others’ FCC IDs, using fabricated test reports. Such behaviors may lead to goods being detained, fines, platform delisting, restricted account or supplier reviews, and subsequent import and listing reviews may also become stricter. The avoidance method is very simple: After obtaining the FCC ID, you can cross-verify through the FCC official website’s Equipment Authorization Database, checking whether the authorization record (Grant), applicant/responsible party, product model, public photos, applicable rules, antenna information, etc. are consistent. Don’t only use “whether the ID can be found” as the sole judgment standard — temporary database updates, incorrect ID format, and inconsistency between the actual product configuration and Grant conditions may all bring compliance risks.
The second type is mismatch between documents and products. For example, the model on the certificate is different from the model you sell, the hardware version is changed but the documents are not updated, the product appearance or key components are changed but not re-assessed. In this case, regardless of whether your product itself is qualified, it will be directly judged non-compliant, because you cannot prove that the product you sell is the one that passed certification. Avoidance method: Before each shipment or model change, check clearly whether the model, hardware version, and key configuration are consistent with those on the documents. If there are changes, assess and update the documents in time.
The third type is non-compliant U.S.-based entities. For example, the US Agent for FCC ID has invalid qualifications, and the U.S. Responsible Party for SDoC does not bear legal responsibility. Many foreign sellers mistakenly think that finding any U.S. agent is enough, resulting in customs clearance rejection and platform delisting. Avoidance method: For FCC ID, a qualified U.S. Agent must be designated for liaison; for SDoC, a U.S.-based Responsible Party that meets legal conditions must bear compliance responsibility, sign formal documents, and include the information in corresponding compliance materials.
The fourth type is non-compliant labels or manuals. For example, the FCC ID label position does not meet requirements, the user manual does not have mandatory FCC warning statements, and usage restrictions are inconsistent with authorization conditions. In this case, rectification will be directly required during spot checks, or even non-compliance will be ruled. Avoidance method: Design labels and user manuals strictly in accordance with corresponding FCC rules, ensure that the label position and content meet requirements, and that warning statements and usage restrictions are consistent with compliance assessment results.
The fifth type is misuse of module certification. Many merchants mistakenly think that having a module FCC ID means the whole device is compliant. In fact, module certification has clear usage restrictions, and when requirements are not met, the whole device will still be judged non-compliant. Avoidance method: Check requirements such as installation, antenna, shielding, and simultaneous transmission against the module’s official integration guide and Grant conditions. If not met, supplement tests or re-apply for authorization in time. For specific requirements, refer to the previous special scenarios chapter.
General Rules for FCC Documents
Regardless of the path, all documents must comply with these general rules:
- Format requirements: Documents must be in English as the standard. Chinese-English comparison is also acceptable, but in case of disputes, the English version shall prevail. Electronic or physical copies are acceptable, but they must be clear and legible, and have relevant seals or signatures to prove validity.
- Validity judgment rules: FCC authorization or SDoC declaration has no fixed “validity period”. Its validity depends on three conditions: ① The current applicable FCC rules have not changed that would invalidate the original compliance conclusion; ② The product’s hardware, software, antenna, structure and other compliance-related configurations have not changed; ③ The model and configuration scope corresponding to the authorization or declaration still cover the currently sold products. As long as all three conditions are met, the document remains valid; otherwise, re-assessment is required.
- Storage requirements: The U.S.-based Responsible Party/Agent must retain corresponding core documents in accordance with FCC rules. Foreign enterprises can store the full set, but must ensure that they can be retrieved within the deadline required by regulators or platforms. The storage period must comply with applicable FCC rules, platform requirements, and the internal management specifications of the Responsible Party. It must cover at least the entire sales cycle of the product and extend to the required period after sales stop. There is no unified universal standard.
10-Minute Quick Self-Check Process
You can spend 10 minutes doing a self-check on your product according to these four steps to find problems in advance:
Step 1: Determine the path. First confirm the functions of your product (whether it has wireless transmission, whether it is an unintentional radiator, whether it meets exemption conditions), and determine the compliance path against applicable FCC rules. If a certified wireless module is used, first confirm whether the module’s usage conditions are met.
Step 2: Verify documents. Check against the document checklist of the corresponding path to see if all core documents are complete, and whether there is compliant U.S.-based entity information (if applicable).
Step 3: Check validity. Verify whether the model, hardware version, and key configuration on the documents are consistent with the products you actually sell. If it is an FCC ID product, cross-verify whether the public information in the FCC official website database matches. Confirm that there are no major changes to the current applicable FCC rules.
Step 4: Match scenarios. According to what you are going to do next — whether it is customs clearance, listing, or responding to spot checks — check whether the corresponding documents are all prepared and can be quickly retrieved.
Self-Check Red Flags (if any of the following occurs, please suspend launch first, complete compliance before proceeding):
- Core authorization documents or supporting test reports cannot be found;
- Product model and key configuration are inconsistent with FCC official records or compliance document records;
- Key compliance components (chips, antennas, power supplies, etc.) of mass-produced products are different from those of test samples;
- Lack of a compliant U.S.-based Responsible Party/Agent (if applicable);
- Conditions such as installation and antenna of the wireless module do not meet the usage requirements of the module authorization;
- Mandatory compliance content in product labels and user manuals is missing.
Summary
After reading this article, you should have mastered the core preparation logic of FCC compliance documents: you can judge the corresponding compliance path according to product functions and rules, list the required document checklist according to the path, prepare corresponding materials for different scenarios such as customs clearance, listing, and spot checks, check the authenticity and validity of documents by yourself, avoid common compliance minefields, and at the same time judge the document supplementary requirements for special scenarios such as using certified modules, product changes, and multi-band devices.
FCC compliance may seem to have numerous items, but its core is actually “matching the path according to rules, ensuring consistency between documents and products”. As long as the basic work is done solidly, the compliance risk in the U.S. market can be significantly reduced.