If you are a Chinese person living in the EU, you may have encountered the situation where your overseas-purchased wireless earphones were detained by customs and you were asked to provide compliance proof; if you are a small seller doing cross-border e-commerce, you may have encountered the platform suddenly removing your Bluetooth products, saying they do not meet RED requirements. Many people think “RED enforcement” is a distant official process, but in fact it is related to everyone who uses wireless devices or sells wireless products. In this article, we will explain the ins and outs of EU RED enforcement in plain language, from the most basic definitions to risk assessment and response methods, to help you build a cognitive system of RED enforcement from scratch, so that you can quickly clarify the direction and avoid core risks when encountering related problems.
1. Introduction to RED Enforcement: Basic Definitions, Jurisdiction, and Core Functions
Core Meaning of RED Enforcement in Plain Terms
First of all, we need to clarify two basic concepts: RED is the abbreviation of the EU Radio Equipment Directive, which sets compliance rules for all wireless electronic devices; while RED enforcement, simply put, is the administrative supervision of already marketed wireless devices by EU authorities — it is not the kind of law enforcement where police arrest people, but the whole process of “spot checks, rectification requirements, and penalties for violations”. Its core goals are to prevent radio interference, ensure personal safety, and rationally use the radio spectrum, and it is currently gradually covering cybersecurity-related requirements.
There are two core points that are most easily misunderstood, which must be clearly explained at the beginning:
First, conformity assessment is not the same as enforcement. Conformity assessment is the process in which an enterprise itself or a third-party institution proves that the product meets the requirements before the product is put on the market, which is equivalent to “pre-test self-check”; enforcement is the official random spot check and verification after the product is put on the market, which is equivalent to “post-exam patrol”, and they are completely two stages.
Second, the CE mark is not an official “exemption from inspection” certificate. Many people think that affixing the CE mark means the product has been officially certified by the EU. In fact, CE is a mark of the manufacturer’s self-declaration that “the product meets EU requirements”. The authorities do not issue CE certificates in advance, and there is no so-called “unified EU RED certificate” — even if you find an EU-accredited notified body for assessment, it does not mean you are exempt from spot checks; you will still be inspected when applicable.
Jurisdiction Scope and Boundaries of Enforcement
Many people’s understanding of what RED regulates is still limited to “devices with Bluetooth and WiFi”, but the scope is much wider than that: as long as it is an electronic device that works by transmitting or receiving radio waves, it is within the jurisdiction, including Bluetooth earphones, routers, smart watches, remote control toys, wireless chargers, walkie-talkies, and even home appliances with wireless functions.
Only two categories are explicitly excluded: one is special equipment with dedicated industry regulations such as military, aviation, and maritime equipment; the other is purely wired electronic devices (such as wired earphones, wired keyboards).
There is also a very important territorial rule called the EU market availability principle — don’t think that just because your company is outside the EU, your warehouse is in China, and you run a direct mail business, you will be fine. As long as EU consumers can normally buy your product: for example, the website supports euro settlement and can deliver to addresses in any EU member state, it is considered to be sold on the EU market and subject to RED jurisdiction. “Overseas shipping” is never a reason for exemption; this rule is specifically targeted at cross-border e-commerce and overseas shopping scenarios.
Why Different Groups Should Pay Attention to RED Enforcement
Some people may say, I’m just an ordinary consumer, just buying something, what does enforcement have to do with me? That’s not the case:
For ordinary consumers, non-compliant wireless devices purchased overseas may be detained by customs, and the losses from return or destruction shall be borne by themselves; even if you get the product, non-compliant devices may interfere with home WiFi and Bluetooth, and even have safety hazards such as charging fires.
For small merchants and cross-border sellers, the consequences are more direct: cargo detention, fines, product removal, full-store recall, and in severe cases, EU-wide sales ban, resulting in all previous investments being wasted.
Moreover, RED’s responsibility coverage is very wide, and not only manufacturers are liable — importers, distributors, and even e-commerce platforms may bear joint and several liability. This is also why platforms actively remove non-compliant products, because they themselves are afraid of being fined.
2. Enforcement Participants: Who Inspects, Who Is Liable
Now that we have clarified what is regulated, next we will talk about the roles in this mechanism, who has enforcement power, and which roles are easily confused.
EU-level Coordinating Role
The European Commission is the maker and coordinator of RED rules, responsible for issuing implementation guidelines, unifying enforcement standards across member states, and resolving disagreements on standard interpretation, equivalent to the “chief referee who sets the rules”. But it does not directly participate in daily spot checks and enforcement, and does not personally inspect goods.
Actual Enforcement Bodies of Member States
The ones responsible for daily enforcement are the agencies of each EU member state, which are mainly divided into two categories:
One is the Market Surveillance Authority (MSA). Each member state will designate a competent authority, such as Germany’s Federal Network Agency (BNetzA) and France’s National Frequency Agency (ANFR), which are responsible for daily market spot checks, handling complaints and reports, and making violation penalty decisions, and are the core enforcement bodies.
The other is customs, which is responsible for preliminary inspection when products enter the country, such as checking whether there is a CE mark and whether basic compliance information is complete. If it finds the product suspicious, it can directly suspend release and hand it over to the market surveillance authority for handling.
A key feature to note here is: the core rules of RED are unified across the EU, but enforcement resources, spot check priorities and penalty rules vary greatly among different member states. Some countries may adopt stricter enforcement measures in specific periods or for specific product categories. Do not assume that if you can sell smoothly in one country, you will definitely not trigger compliance issues in another country.
Division of Roles and Responsibilities of All Parties
In addition to official agencies, there are several often-mentioned roles that many people mix up. We will clarify them all at once here:
- Notified Body: Many people think it is an official agency, but in fact it is a third-party compliance assessment body accredited by the EU, only responsible for pre-market conformity assessment of some high-risk products. It is not an enforcement agency at all and has no power to inspect goods or issue fines. To check the authenticity of a notified body’s qualification, you can verify it in the EU’s official NANDO database (official notified body qualification query system).
- Authorised Representative (often referred to as “EU Responsible Person”): If an overseas manufacturer has no entity established in the EU, it can designate an authorised representative within the EU as the regulatory liaison window through a written agreement, responsible for cooperating with regulatory authorities’ inquiries, and providing and properly keeping compliance documents as required. It should be noted that the authorised representative is only one type of economic operator within the EU; importers, fulfillment service providers that meet specific conditions, etc., also need to bear corresponding obligations according to regulations; and no matter which type of EU-based entity it is, it does not exempt the manufacturer from the primary compliance responsibility. The core obligations of product design, testing, and issuing the declaration of conformity still lie with the manufacturer.
- Manufacturer: Bears primary compliance responsibility; product design, testing, and issuing the Declaration of Conformity (DoC, the product compliance commitment letter signed and sealed by the enterprise itself) are all obligations of the manufacturer.
- Importer: Equivalent to the “gatekeeper” for EU entry, it must confirm that imported products have completed compliance procedures and retain relevant documents. The importer is also liable if there are problems with the product.
- Distributors/E-commerce Platforms: Must not sell obviously non-compliant products, and must cooperate in providing information during regulatory investigations, otherwise they will also be penalized.
3. Triggers and General Process of RED Enforcement
Many people wonder how RED enforcement comes to them, is it only “bad luck” to be picked? In fact, there are several common trigger scenarios, and the handling rhythm varies by scenario.
Common Trigger Scenarios and Enforcement Differences
The most common is customs entry spot check — whether it is merchants importing in bulk or individual overseas shopping, as long as the goods enter EU customs, they may be picked. Unqualified goods are directly detained, and you can either supplement documents to apply for release, or have the goods returned/destroyed.
The second is market circulation spot check: regulatory authorities randomly sample and inspect products from offline stores, e-commerce platforms, and third-party warehouses. The intensity will increase significantly during peak consumption seasons (such as Black Friday, before Christmas) or special rectification periods. Generally, they first require removal from shelves, then conduct further investigation.
The third is triggered by complaints and reports — consumers, peers, and industry associations can all report non-compliant products. Regulators will launch verification after receiving reports, usually first requiring suspension of sales before investigation.
The fourth is accident/interference report — if the device causes electromagnetic interference (such as interfering with medical or emergency communications), safety accidents or cybersecurity incidents, regulators will directly intervene, and the speed is very fast.
The fifth is special rectification: the EU or individual member states conduct centralized inspections on high-risk products (such as high-power wireless devices, children’s wireless toys). During this period, the probability of such products being inspected will rise sharply.
Four-Step General Enforcement Process (Plain Language Version)
Once inspected, the general process is only four steps, not as complicated as everyone thinks:
The first step is sampling/detention + preliminary verification. The regulatory authority either samples products from the market, or directly detains suspicious batches, and first checks the easiest to verify content: such as whether the CE mark is standardized, whether there is manufacturer and EU responsible person information, and whether packaging labels are complete.
The second step is in-depth document verification. If there are doubts in the preliminary verification, or the product is a high-risk category, the regulator will require the provision of a full set of compliance documents, including DoC, technical files, test reports, etc. The details checked include: whether the test report model is consistent with the actual sales model, whether the test standard is expired, and whether the test covers all wireless functions.
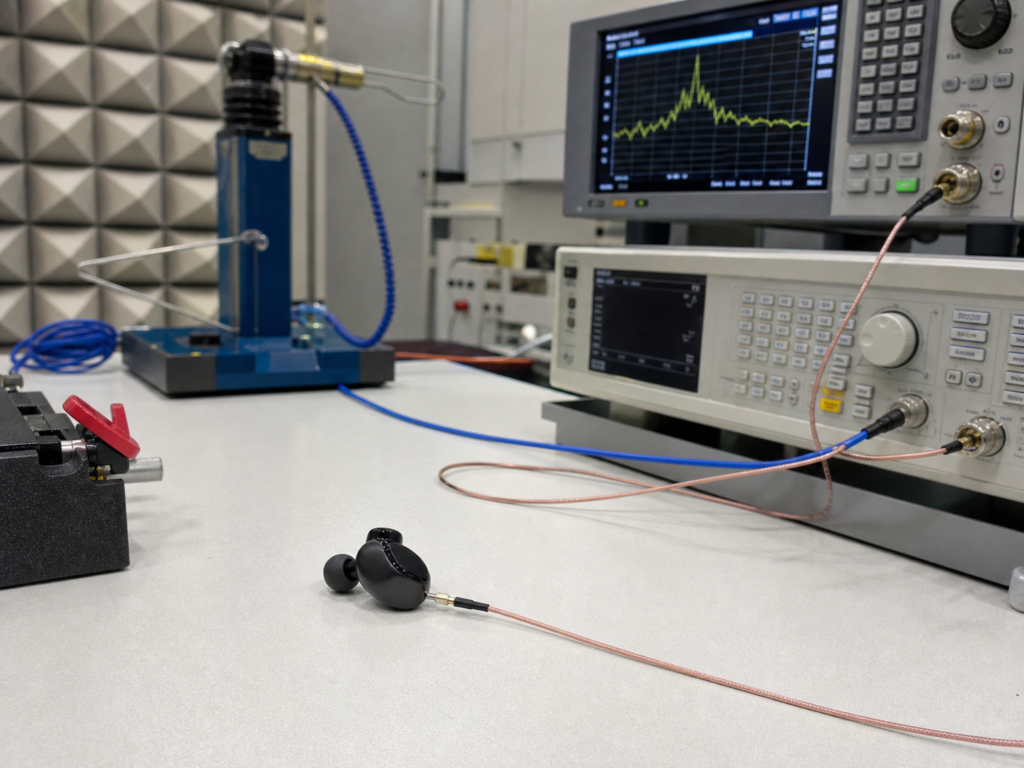
The third step is physical testing — this step is not mandatory. Only when the documents are questionable, the product is high-risk, or there are substantive problems reported, will the sample be sent to an accredited laboratory for testing. The content includes transmit power, frequency band used, electromagnetic compatibility, safety indicators, etc.
The fourth step is result notification and disposal. If the verification is qualified, the goods will be released or sales will be resumed; if unqualified, rectification or penalty requirements will be given according to the degree of violation.
4. Types of RED Violations and Corresponding Handling Results
Many people are most concerned about the consequences of violations. RED violations are graded: minor ones only need correction, while severe ones may lead to direct EU-wide sales ban. Specifically, they can be divided into three categories:
| Violation Level | Common Situations | Typical Handling Methods |
|---|---|---|
| Minor violation (formal/document issues) | Non-standard CE mark, incomplete label information, missing local language version of the manual, defective documents but the product itself is compliant | Deadline to supplement documents, re-label, modify the manual, release/resume sales after passing verification; whether a fine is imposed depends on member state regulations and specific circumstances |
| Moderate violation (substantive issues that can be rectified) | Slightly excessive parameters, non-standard test reports but can be re-tested, correctable differences between model and documents, failure to implement applicable cybersecurity requirements | Remove from shelves for rectification, recall sold products, pay fines; active cooperation and active recall can lead to lighter handling |
| Serious violation (non-rectifiable/high risk) | Using frequency bands prohibited by the EU, forging CE/test reports, deliberate fraud, major safety/interference risks, refusing to cooperate with enforcement | Confiscate and destroy goods, permanent sales ban, high fines, inclusion in Safety Gate (EU-wide rapid alert system for dangerous products, formerly known as RAPEX; a notification from one country leads to synchronized control across the EU), inclusion in regulatory blacklist |
There are two details that need special explanation here:
First, regarding fines, the EU has no unified standard. Each member state determines the fine according to its own regulations, violation circumstances, and product sales volume. The common range is several thousand to hundreds of thousands of euros, and fines for particularly large sales volume will be higher.
Second, the boundary of criminal liability: the vast majority of RED violations are administrative penalties. Only in very few cases — such as deliberate fraud causing major safety accidents — may involve criminal liability under member state laws. There is no need to worry about jail time for ordinary violations.
5. Self-Assessment Method for RED Enforcement Risks
You don’t need to understand complex technology. Follow three steps of self-inspection to complete preliminary risk screening and quickly identify obvious compliance loopholes, but this cannot replace professional laboratory testing or formal compliance assessment.
Step 1: Confirm whether it falls within RED jurisdiction
The judgment logic is simple: first check whether the product works by transmitting/receiving radio waves — if yes, it may be within the scope; then exclude special equipment such as military, aviation, maritime equipment and purely wired equipment; finally confirm whether it is sold to the EU market (meeting the availability principle).
A special case to note: individual overseas shopping of 1-2 units for personal use generally does not trigger enforcement, but high-risk devices (such as high-power walkie-talkies) may be intercepted due to interference/safety risks; if multiple units are sent at one time and determined to be for sale, they will be handled according to merchant standards.
Step 2: Self-check compliance basics against enforcement verification priorities
No need to test technical parameters, first check these basic items that are most prone to problems:
- Appearance labels: Is the CE mark clear and standardized? Is the name and address of the manufacturer and EU responsible person indicated on the product or packaging?
- Compliance documents: Is there a DoC declaration of conformity? Does the test report model correspond to the actual sales model? Is the test standard within the validity period?
- Wireless parameters: Does the frequency band used fall within the common allowed range in the EU (such as 2.4GHz WiFi and classic Bluetooth are widely used compliant frequency bands)? But note that frequency band compliance is only the foundation. Final compliance also depends on maximum transmit power, channel range, occupied bandwidth, antenna configuration, whole-machine test results and applicable harmonized standards; some member states may also have additional restrictions on specific frequency bands. You cannot directly determine product compliance just because the frequency band is common.
- User materials: Does the manual have a language version of the target member state? Is there information such as the frequency band used and maximum transmit power?
Step 3: Judge risk level combined with scenarios
Even if the product is under RED jurisdiction and basic compliance is done, the probability of being inspected varies by situation. It can be judged from three dimensions:
- Product attributes: High-risk products (cellular communication devices, high-power wireless devices, children’s wireless products) > low-risk products (wireless mice, Bluetooth earphones, ordinary remote controls); products with multiple wireless functions > products with single wireless function.
- Sales scenarios: E-commerce platforms > offline physical stores; large sales volume covering many countries > small sales volume in a single country.
- External environment: Member states with strict supervision > member states with looser supervision; the probability of being inspected during peak consumption seasons and special rectification periods is higher than daily periods. For key rectification categories, please refer to the relevant description of enforcement trigger scenarios above.
Quick Identification of High-Risk Violation Pitfalls
There are several very typical high-risk pitfalls that can be identified at a glance, and you must avoid them when encountered:
For example, pasting fake CE marks, or using test reports from other products or other regions (such as US FCC) — FCC is US certification, which is not recognized by the EU at all;
For example, no EU responsible person, or the responsible person’s information is false and cannot be contacted at all, which is the most common mistake made by many small cross-border sellers;
For example, the actual transmit power and frequency band used by the product are completely inconsistent with the declaration, such as deliberately adjusting the router power to exceed EU standards for better signal;
For example, only the wireless module has RED certification, but there is no whole-machine compliance certificate — many people think that if the module has passed RED, there is no need to test when installed in the whole machine. But in fact, the structure of the whole machine and antenna position will affect wireless parameters, so whole-machine verification must be done.
6. Basic Response and Pitfall Avoidance When Encountering RED Enforcement
If you really encounter RED enforcement, don’t panic. Remember a few core principles to minimize losses.
Core Actions to Take Immediately
First, verify the identity of the enforcement party. Now there are many scammers pretending to be EU regulatory authorities sending emails saying products are non-compliant and need to pay fines, asking to transfer money to private accounts. In this case, be sure to ask the other party to provide an official enforcement notice with official document number, seal and handler information. If you are unsure, you can check the contact information on the official website of the corresponding regulatory authority to verify. Do not click links in unfamiliar emails or transfer money casually.
Second, organize documents and actively cooperate. Sort out DoC, test reports, and EU responsible person information. Do not conceal, let alone provide fake documents — cooperating with the investigation and timely supplementing real documents can be used as a reference factor for discretionary mitigation of penalties in some cases in some member states; if you conceal or falsify, originally minor violations may be upgraded to serious violations.
Response Priorities for Different Scenarios
If it is customs cargo detention, be sure to submit complete compliance documents as soon as possible. If necessary, contact the EU responsible person to help liaise with customs to strive for early release. The longer you delay, the more troublesome it is, and finally the goods may be directly returned or destroyed.
If it is market/platform spot check, be sure to submit documents within the time limit required by the regulator or platform. If there are indeed small problems, actively propose a rectification plan, and do not resist. If the e-commerce platform removes the product, first go through the platform appeal process to submit documents, and at the same time cooperate with the regulatory investigation. Absolutely do not secretly change links or rename the product to re-list — if found, it will be directly treated as a serious violation, and even the entire store will be banned.
Minefields That Must Never Be Stepped On When Responding
There are several mines that will only make things worse, and must be avoided:
First, do not delay submitting documents. Exceeding the time limit given by the regulator will directly increase the penalty.
Second, absolutely cannot privately transfer or exchange detained goods. This is a serious illegal act. Originally it was just a product compliance issue, but finally it may become a problem of obstructing law enforcement.
Third, do not pretend to understand and casually explain technical issues — for example, if you are not sure whether a certain frequency band is compliant, you make random promises, and finally it is found that there is indeed a problem, it will be considered deliberate concealment. For technical issues, it is best to find professional compliance personnel or the EU responsible person to liaise.
Fourth, absolutely cannot buy fake reports or fake certificates to muddle through — now regulatory authorities can check the qualifications of testing institutions and notified bodies, and fake reports are caught every time. If found, they will be directly treated as serious violations, which is not worth the loss.
Applicable Situations and Channels for Appeal
If you think the penalty is wrong, of course you can appeal, but it must meet the conditions: for example, non-standard testing methods, the tested sample is not the actual sales model, or there is sufficient evidence to prove product compliance. In these cases, you can apply for review.
The appeal channel is to first apply for review to the regulatory authority of the member state that issued the penalty; if you still have objections to the review result, you can continue to handle it according to local administrative relief or judicial litigation procedures. If the case involves special circumstances such as cross-member state enforcement coordination, disputes over RED rule interpretation, or objections to Safety Gate notifications, you can also consult or report to relevant channels of the European Commission on the basis of completing the local procedures of the member state, but the European Commission will not directly overturn the compliance penalty decision made by the member state’s regulatory authority.
7. Common Misconceptions and Core Competence Summary
5 Most Frequent Cognitive Misconceptions
Finally, we sort out the most common misconceptions about RED enforcement, and many people fall into traps because of these:
- Misconception: With a CE mark, you will not be inspected — Correct answer: CE is a self-declaration, enforcement is random spot checks, and you can only pass by presenting complete evidence to prove compliance.
- Misconception: RED enforcement is only related to manufacturers — Correct answer: Importers, distributors, and e-commerce platforms all bear joint and several liability. Individuals who buy a large number of goods overseas and are determined to be for sale will also be inspected.
- Misconception: RED requirements are completely different in each EU country — Correct answer: Core technical requirements are unified across the EU, and only the tightness of enforcement, penalty intensity, and language requirements differ.
- Misconception: With a test report/notified body certificate, you are permanently compliant — Correct answer: The report is only responsible for the tested sample and the current effective standard; product design changes and standard updates will invalidate it.
- Misconception: Small-batch sales/only online sales will not be inspected — Correct answer: E-commerce is the current focus of enforcement. Regulators can directly place orders on platforms to sample, and small batches may also trigger inspections by customs or complaints.
Things You Can Independently Judge After Learning
After establishing a complete understanding of RED enforcement, you can independently complete these basic judgments and operations: you can judge whether a product falls within the scope of RED enforcement jurisdiction, initially assess the level of RED enforcement risk of a product, identify necessary compliance documents and quickly find common fraud pitfalls, know what to do immediately and which mines to avoid when encountering RED enforcement, distinguish the approximate consequences of different violation levels, and know when you can handle basic problems by yourself and when you need to find professional support. Essentially, the core logic of RED enforcement is that the EU does not provide “official certification endorsement” for products in advance, but enterprises bear primary responsibility for the compliance of their own products, and through post-market spot check supervision and violation cost constraints, enterprises are forced to actively implement compliance requirements.
Advanced Official Information Query Channels
If you need to check more authoritative official information, you can go to these channels: the European Commission official website can check the latest RED rules and implementation guidelines; the NANDO database can check the authenticity of notified body qualifications; the official website of the target member state’s regulatory authority can check local specific enforcement requirements and complaint channels; the Safety Gate official website can check non-compliant products that have been notified by the EU to avoid pitfalls.